SC-200 Study Guide 2026: A Six-Week Plan to Pass

The short answer
The SC-200 study guide for 2026 starts from Microsoft's skills measured as of 21 October 2026, which split the Security Operations Analyst exam into three areas: manage a security operations environment (40-45%), respond to security incidents (35-40%) and perform threat hunting (20-25%). A score of 700 or more passes. Plan about six weeks of study, put Kusto Query Language (KQL) at the centre because it runs through all three areas, practise in a free Azure lab, and finish with Microsoft's free practice assessment and exam sandbox before you book.
Exam facts were read on Microsoft Learn on 11 October 2026 (October 2026). Microsoft, Sentinel, Defender and SC-200 are Microsoft's marks. EDWartens is not a Microsoft training partner.
What the 2026 outline covers
Microsoft's SC-200 study guide lists the skills measured as of October 21, 2026. Most questions cover features that are generally available, but commonly used preview features can appear. Read the page again on the day you book, because outlines are revised several times a year and the English exam changes first.
Skill area | Weight | What it covers |
|---|---|---|
Manage a security operations environment | 40-45% | Defender XDR and Sentinel automation, Defender for Endpoint settings and ASR rules, Sentinel roles, retention tiers, workbooks, SOC optimization, data connectors, analytics and custom detection rules |
Respond to security incidents | 35-40% | Incidents in Defender XDR, Office 365, Identity, Cloud Apps, Entra, Purview and Defender for Cloud, agentic AI with Security Copilot, case management, device timelines and live response |
Perform threat hunting | 20-25% | Choosing the right table, KQL, Advanced Hunting, threat analytics, hunting graphs and blast radius, Sentinel graph, data lake KQL jobs, summary rules, notebooks and the Sentinel MCP server |
Two themes are new for many candidates. Security Copilot and its agents now sit inside the incident area, and the hunting area expects the Sentinel data lake: KQL jobs, summary rules and notebooks. Older video courses recorded before 2026 rarely cover either.
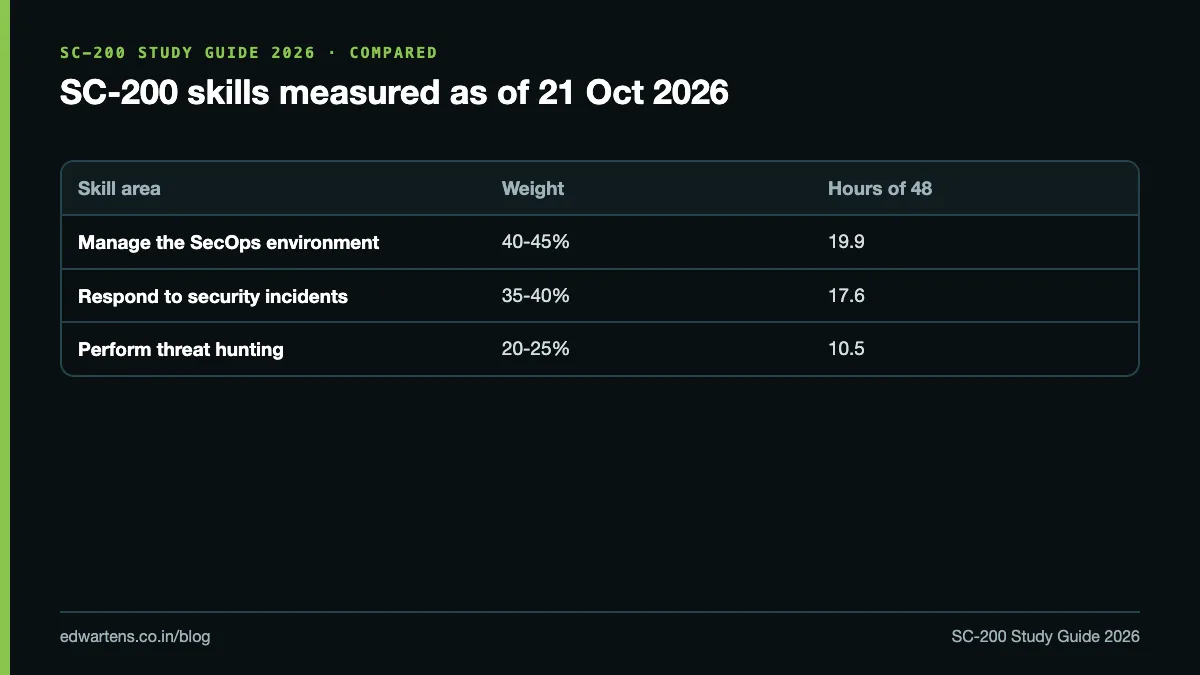
Worked example: sharing 48 study hours by weight
You have six weeks and about eight hours a week, so 48 hours. Share them in proportion to the midpoint of each published range.
- Midpoints: 42.5, 37.5 and 22.5. They add up to 102.5, not 100, because the ranges overlap, so divide by 102.5.
- Manage the environment: 48 x 42.5 / 102.5 = 19.9 hours.
- Respond to incidents: 48 x 37.5 / 102.5 = 17.6 hours.
- Threat hunting: 48 x 22.5 / 102.5 = 10.5 hours.
- Check: 19.9 + 17.6 + 10.5 = 48.0 hours.
Then move a few hours to whichever area your practice assessment shows is weakest. Hunting carries the smallest weight, but KQL questions appear across all three areas, so the KQL hours pay twice.
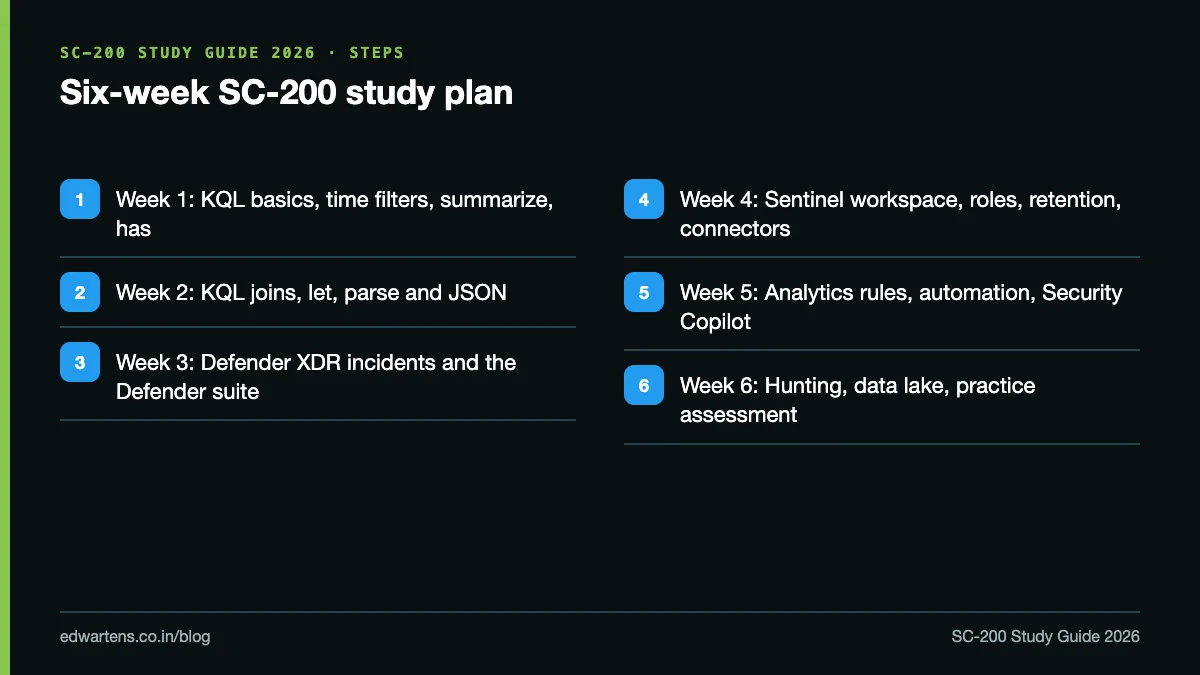
A six-week plan
Week | Focus | Done when you can |
|---|---|---|
1 | KQL from the first query | Filter on time first, summarize, use has rather than contains |
2 | KQL joins, let, parse and JSON | Explain why the default join removes duplicate left keys |
3 | Defender XDR incidents, Endpoint, Office 365, Identity, Cloud Apps | Work an incident from attack story to classification |
4 | Sentinel workspace, roles, retention, connectors | Pick the right connector and table for a source |
5 | Analytics rules, automation rules, playbooks, Security Copilot | Set frequency and lookback so late events are not missed |
6 | Hunting, data lake, notebooks, practice assessment | Score well on Microsoft's free practice assessment twice |
KQL: the skill that carries the exam
KQL is the read-only query language behind Microsoft Sentinel, Advanced Hunting, Log Analytics and Azure Data Explorer; Microsoft's KQL overview describes a Kusto query as a read-only request that never writes data. A query starts with a table and passes it through operators joined by the pipe character. Three habits win marks:
- Filter on time first, then on the most selective value, then aggregate. Sentinel tables use TimeGenerated; Defender XDR tables in Advanced Hunting use Timestamp.
- Prefer has to contains. The has operator looks up indexed terms of three or more characters, while contains scans every string.
- Know your joins. The join operator defaults to innerunique, which removes duplicate keys from the left table before matching, and leftanti answers "seen here but never there" questions.
A second worked check worth knowing: a scheduled analytics rule that runs every 5 minutes with a 10-minute lookback runs 1,440 / 5 = 288 times a day, and each event is read by 10 / 5 = 2 runs. Set the lookback equal to the frequency and late-arriving events can fall between runs and never be evaluated.
Sentinel now lives in the Defender portal
Learn the Defender portal navigation first. Microsoft's page on Sentinel in the Defender portal says Sentinel is generally available there, including for customers without Defender XDR or an E5 licence, and that after 31 March 2027 Sentinel will no longer be supported in the Azure portal. Exam questions increasingly name Defender portal pages.
A lab that costs little or nothing
- KQL practice: the Azure Data Explorer help cluster has a free Samples database that anyone with a Microsoft account can query.
- Sentinel: an Azure free account and a new Log Analytics workspace with the time-limited Sentinel free trial. Check the current trial terms on Microsoft Learn, set a daily cap and delete the resource group when you finish.
- Defender XDR: trial licences where your region and account allow. Availability changes, so check the trial page.
Booking and honesty
The exam is booked through Microsoft and the fee is paid to Microsoft, at a price set for the country where you sit it. Microsoft's certification page shows a 12-month renewal cycle, and associate certifications are renewed free through an online assessment on Microsoft Learn. Use Microsoft's free practice assessment and the exam sandbox. Never use exam dumps: they break Microsoft's exam rules and teach you nothing you can use in a SOC.
Is SC-200 worth it in India?
Indian banks, insurers, IT services firms and managed security providers that run Microsoft 365 E5, Defender and Sentinel hire security operations analysts who can write KQL and work incidents in the Defender portal. SC-200 is a clear signal for those roles, especially paired with a hunting portfolio. If you are newer to security, start with our ISC2 CC exam prep study plan; if you want the same hunting method on an open source SIEM, read our Wazuh threat hunting tutorial.
Prepare free
The free Microsoft Sentinel and Defender: SC-200 Exam Prep course maps fourteen modules to the October 2026 outline: KQL from first query to hunting, Defender XDR incidents and attack disruption, Endpoint, Office 365, Identity and Cloud Apps, Purview investigations, Sentinel setup, connectors, analytics rules, automation, Security Copilot and the data lake. It uses Microsoft Learn's own SC-200 videos with original notes, worked problems and original practice questions.
It is a free course with a verifiable certificate of completion, and anyone can check a certificate on our verification page. It is not the Microsoft certification, which only Microsoft awards after its own exam, and EDWartens is not affiliated with Microsoft. Start the SC-200 exam prep course.
For classroom practice, our PLC course in Bangalore: syllabus and duration sets out what is taught and for how long.
Frequently asked questions
Q: What is on the SC-200 exam in 2026?
A: Under the skills measured as of 21 October 2026, SC-200 tests managing a security operations environment (40-45%), responding to security incidents (35-40%) and threat hunting (20-25%) with Microsoft Defender XDR, Microsoft Sentinel and KQL.
Q: What score do I need to pass SC-200?
A: Microsoft's study guide says a score of 700 or greater is required to pass.
Q: How long should I study for SC-200?
A: About six weeks at eight hours a week suits someone who already knows basic networking, Windows logs and incident response. Spend roughly 20 hours on managing the environment, 18 on incident response and 10 on hunting, and adjust after a practice assessment.
Q: Do I need to learn KQL for SC-200?
A: Yes. KQL runs through all three skill areas: detection rules, investigations and hunting all use it. Practise free on the Azure Data Explorer help cluster before you build a Sentinel lab.
Q: Does the SC-200 certification expire?
A: Microsoft's certification page shows a 12-month renewal cycle. Associate certifications are renewed free by passing an online renewal assessment on Microsoft Learn.
Q: Is there a free SC-200 course with a certificate?
A: Yes. EDWartens' SC-200 Exam Prep is a free course with a verifiable certificate of completion. It is not the Microsoft certification, which only Microsoft awards after its own SC-200 exam.
Learn this, free
The courses that teach this
Every lesson, the written notes and the practice are free with an account. Only the certificate is optional and paid.


